

FILTERED RESULTS
FILTERS
MCap $2.8T 0%24h Vol $51.5B +10%Fear & Greed 61/100Alts Index 55/100
BTC.D 59.7% +0.5%Stable.D 9.4% 0%ETH.D 11.0% +0.1%Others.D 19.9% -0.6%
S$0.0649+41%•W$0.0231+31.35%•BAT$0.1598+22.22%•GRASS$0.7834+20.64%•STRK$0.1178+18.2%•CARDS$0.3172+15.25%•PLUME$0.0216+14.97%•CFX$0.0675+12.26%•EIGEN$0.2637+10.57%•ETHFI$0.7445+8.78%•
APEPE$0.00000129-11.27%•BP$1.115-9.2%•DRV$0.5065-7.49%•Q$0.0289-6.99%•KAIA$0.0520-6.89%•AKE$0.0261-4.53%•PONS$0.3502-4.15%•ATOM$1.926-3.26%•IMX$0.1927-2.6%•SAND$0.0657-2.55%•
•
·
·
FILTERED RESULTS
User Exposes Hidden Hardware Implant in European Ledger Wallet
XRP’s next Wall Street expansion comes with an unexpected complication from Ripple
XRP Ledger Fixed a Bug From 2015 That Could Have Created…
Solana Dominates Tokenized Equities Trading with 65% Market Share
Monetary Authority of Singapore Places Hyperliquid on Investor Alert List
Russia’s Moscow Exchange Pilots Crypto Trading for December Launch
Ledger Confirms Hardware Implant as Tampered Wallet Reports Allegedly Spread to Europe
Ledger Investigates Hardware Implant Reports Linked to Southeast Asian Reseller
CFTC Unveils New Framework for Crypto Trading Amid Legal Concerns
Bought a Ledger From a Reseller? 5 Checks After the $86…
Everyone wants SCOTUS to take up prediction markets: State of Crypto
XRP Ledger developers disclosed a decade-old payment engine bug that could have minted
Some Kraken futures limit orders can still fill after a successful cancel
US threatens to block weapons supplies to Ukraine over attacks on...
Ledger Confirms Draining Cases Linked to CryptoBilis-Sold Devices
Bitcoin Price Eyes $85K, but Momentum Has Yet to Show Up
Ledger Reports $72 Million in Losses Linked to Compromised Devices from Reseller CryptoBilis
Tokenized Stocks Show Real Demand But Remain Volatile and Illiquid, IMF Finds
Saylor teases Strategy Bitcoin buying after ending September with STRC buybacks
Tokenization Hits $65 Billion, but the IMF Warns of New Vulnerabilities
Bitcoin ETF Weekly Outflows Hit 3-Month High, Ethereum Funds Extend Losing Streak
Bitcoin hedge funds face a liquidation trap when their collateral is split across markets
BTC breaks above $84,000, up 0.16% on the day
Starknet (STRK) traded at $0.1128, up 50.47 percent, at…
4,499 $BTC (377,172,944 USD) transferred from unknown wallet to unknown new...
*S&P 500 OPENS UP 1.1%, NASDAQ GAINS 1.3% ...
Bitcoin, Ethereum and Solana ETFs All in the Red for October
Papertrade Addresses Price Manipulation Concerns Amid Protocol Adjustments
Kyrgyzstan Orders Liquidation of Gold-Backed Stablecoin Issuer and Crypto Exchange
Liquid Bitcoin Redemptions Remain Frozen Amid Reserve Coverage Issues
Papertrade Implements Stricter Trading Limits Following Manipulation Claims
Clarity's failure could speed crypto innovation while shielding incumbents
Tokenized stocks can carry the same rights without the same trading protections
Liquid Network peg-outs remain frozen 35 days after Elements exploit drained nearly 4,000...
PaperTrade responds to fairness and manipulation concerns: queue mechanism ensures fairness, some users manipulating BBO could not sustain profits
Liquid Network at 86% Backing as Bitcoin Redemption Freeze Drags On
President Trump declares 'energy ceasefire' between Russia and Ukraine
Analyst: Bitcoin may need to break through $84,000–$85,000 to determine its next move
Trump Says Russia And Ukraine Have Reached ‘Energy Ceasefire’...
IMF Reports Lower Liquidity and Higher Volatility for Tokenized Stocks Compared to Traditional Stocks
PeckShield Links $3.89 Million Ledger Wallet Theft to Binance Deposits
Bybit's Weekly Platform Updates General• Keynote with Ben: new products + upgrades on Oct 13• Ask ...
Ledger supply chain attack suspected of spreading to Europe, user reports hardware implant found in device from official reseller
Ripple ETFs Defy Crypto Slump With Another Green Week but XRP Price Sinks
ESMA Wants Proof Tokenised Collateral Can Be Cashed Out in a Crisis
XRP ETFs extend a 13-week inflow streak as Bitcoin, Ethereum and Solana funds shed $1.25 billion
Trump Announces 'Energy Ceasefire' Agreement in Russia-Ukraine War
Cheaper AI Could Make Computing Power More Expensive — Grayscale
Tom Lee says Ethereum "should top $5,000" by the end of 2026...
More Orange: Saylor Hints at Growing Strategy’s 848K Bitcoin Stash
SpaceXAI Official Account Renamed to SpaceX Super Intelligence
XRP Ledger Reveals Long-Standing Bug That Could Have Minted Trillions
XRPL Fixes Decade-Old Bug That Could Have Minted Trillions of XRP RippleX and the XRP Ledger...
*US MARCH CONSUMER CONFIDENCE 91.8; EST. 88.0 ...
New iPhone spyware can hunt for crypto wallets and extract their data every 15 seconds
One Year After Crypto’s $19 Billion Liquidation,…
Coldcard Investigates Phishing Post From Official X Account After Earlier Seed-Generation...
*US FEB. JOB OPENINGS 6.882M; EST. 6.918M ...
Coldcard X Account Hit by Phishing Scam After $100M Fiasco
U.S. Treasury Secretary Confirms No Expected Military Conflicts Before Midterm Elections
US Bitcoin ETFs Experience Significant Withdrawals Amid Market Reversal
China Announces They Will Build A New National Blockchain Network, Alongside A National Integrated...
US Treasury Secretary Bessent: Trump expects no military conflict before midterm elections
IMF finds demand for tokenized stocks, says the market is still volatile, illiquid
How Zcash Plans to Hide Your Keys From AI and Quantum Attacks
Strangely Rational — Week in Review
What happens when crypto trades stocks while Wall Street sleeps?
Market Overview: BTC : $83032 ETH : $2502.27 BNB : $748.63 SOL : $109.39 Market Cap :Total :...
A whale placed a $22.89 million BTC buy order on Binance spot at $82,975
Lightning apps using unpatched LDK risk Bitcoin theft from a reconnect lie


Lightning Development Kit (LDK), a library for building Bitcoin Lightning wallets and payment applications, has patched a flaw that could let a malicious channel peer steal the value of a forwarded payment by lying after reconnecting. Affected application developers need to incorporate the fix into the software they deploy.
The October 1-dated v0.2.7 and v0.1.13 security releases address the LDK reconnect vulnerability on the 0.2 and 0.1 branches, respectively. Bitcoin Optech described the fixes in its Oct. 9 newsletter.
How the LDK reconnect flaw could cost Bitcoin
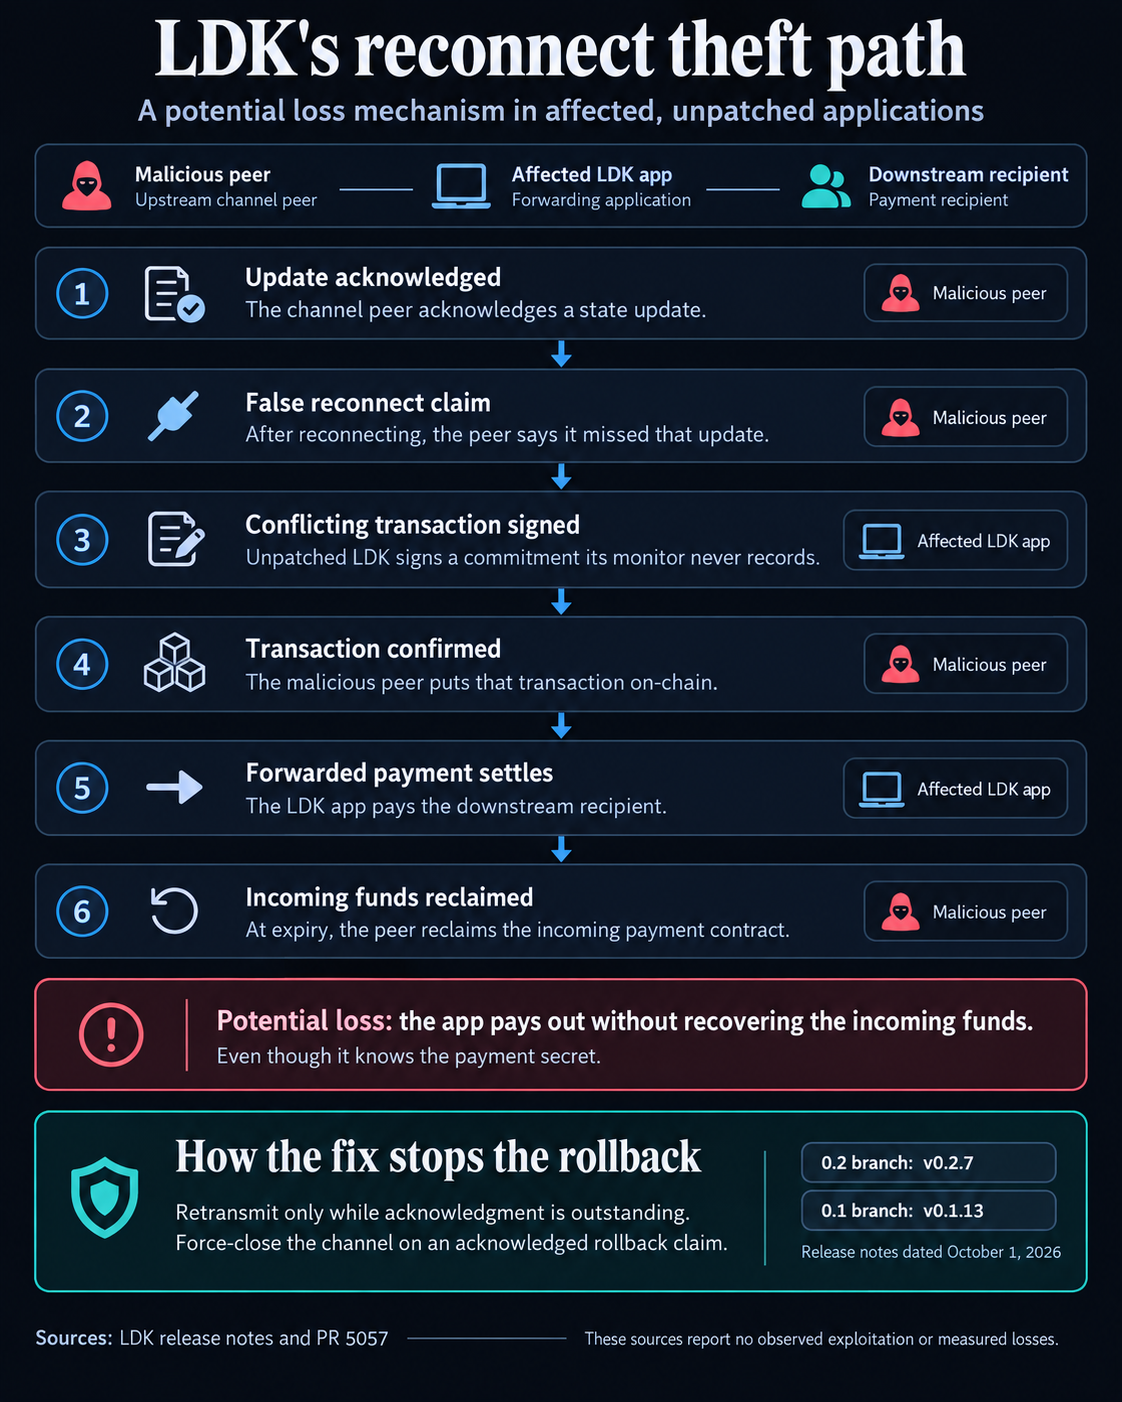
The attack starts with a channel peer acknowledging an update, then reconnecting and pretending it never received it. Before the fix, that false claim could cause LDK to sign a conflicting commitment transaction.
A commitment transaction represents a channel's agreed state and can be used to settle it on Bitcoin's blockchain. In the scenario described in PR 5057, the newly signed transaction was not recorded by LDK's channel monitor, the component tracking the channel's on-chain claims.
That gap could turn a forwarded payment into a loss. The malicious sender could confirm the transaction on-chain and let the payment settle with the next recipient. It could then reclaim the incoming payment contract when it expired, even though the forwarding node knew the secret normally used to claim payment.
The forwarding application would have paid downstream without recovering the corresponding incoming funds. The fix permits retransmission only while the peer's acknowledgment remains outstanding and force-closes the channel when the peer claims an already-acknowledged update was missed.
Alongside the LDK reconnect fix, version 0.2.7 addresses a different theft path involving LSPS2 just-in-time payments, where a liquidity service opens a channel as part of handling a payment.
An intercepted payment could misrepresent its amount, causing the service to open a channel and forward more Bitcoin than the incoming payment supplied. The service would cover the difference from its own funds. PR 5042 addresses that amount check.
That exposure concerns the LSPS2 service flow. The v0.1.13 notes list the shared reconnect fix without listing the LSPS2 fix.
These defects differ from the splice-fee diversion and saved-state loading bugs covered in CryptoSlate's Sept. 13 LDK v0.2.6 report. Core Lightning is a separate implementation, as described in the update below.
LDK’s architecture documentation explains that the SDK is compiled and executed inside applications. Developers must incorporate the relevant patched library code into deployed software. For LSPS2 integrations, the PR 5042 commit explanation flags that payment contracts queued by a prior version retain unvalidated amounts; teams need to account for those pending contracts as well as updating the library.
Source: CryptoSlate